How Much Authority Should an AI System Really Hold? A Plain-English Introduction to SACM

The MORAL/CPM Management Portfolio Map: Martin Steiner’s illustrative manager’s view of delegated AI authority. The map is marked “Illustrative, replace data”; it is a discussion aid, not a recommended profile for any organisation.
When an organisation considers using an AI agent, one question tends to come first: how autonomous is it? Can it only suggest an action, or can it carry it out?
That matters, but it does not tell the whole story. An agent might be permitted to complete routine tasks independently while being kept away from decisions with serious consequences. Another might have limited independence yet still influence an important decision through the information it selects or the recommendations it presents.
A useful AI governance framework therefore needs to ask two questions together: how independently may a defined function operate, and which consequences may it touch? The Steiner AI Authority & Consequence Matrix (SACM) is a proposed framework for making those boundaries clearer.
Capability is not authority
A system’s capability describes what it can do. Delegated authority describes what it is permitted to do in a particular setting.
The distinction is practical. A system might be technically able to prepare and send a payment, but an organisation could authorise it to prepare a transaction only, with a person required to approve the transfer. The system’s capability has not changed. Its permitted role has.
SACM treats the function, not the system as a whole, as the unit to assess. A procurement agent, for instance, might search for suppliers, shortlist them and approve expenditure. Those are different functions, and they need not receive the same authority. A single label for the entire system can conceal these differences.
OAL: how independently can the function operate?
SACM uses Operational Autonomy Levels (OAL) to describe how independently one defined function operates in its actual context. The levels run from OAL-0 to OAL-5:
- OAL-0, Tool: produces an output in response to a human instruction, without independent operational progression.
- OAL-1, Advisory: supports a human task; the human directs consequential steps.
- OAL-2, Controlled: develops a recommendation or prepares an action, but needs explicit human approval before commitment.
- OAL-3, Supervised: executes defined tasks within bounded discretion and escalation rules.
- OAL-4, Delegated: pursues operational goals and commits actions within a declared mandate and limits.
- OAL-5, Executive: exercises broad goal-setting or resource authority normally associated with senior accountable decision-making.
These levels answer a question about independence, not about the seriousness of an outcome. OAL-4 does not, by itself, say whether a function should be trusted with a minor administrative task or a decision with major consequences. That is why SACM pairs OAL with consequence classes and permissions.
Consequence classes: what could be affected?
SACM groups credible adverse consequences into four classes. The class is about the nature and effect of a consequence, not simply its financial value:
- C1, Limited: readily reversible, with limited internal, financial or operational effect.
- C2, Material: meaningful but reasonably recoverable customer, operational, administrative or financial effect.
- C3, Major: substantial financial, legal, employment, data, commercial, reputational or operational effect that may be difficult or costly to reverse.
- C4, Critical: potential material effect on safety, fundamental rights, critical infrastructure, major environmental outcomes, systemic stability or organisational survival.
The boundaries need judgement. A low-value action can still have a major effect on someone’s rights or opportunities. And a change that can be reversed technically may not undo its practical effects if people have already acted on it.
The classes also help organisations consider accumulation. Many small decisions may add up to a more consequential pattern, so a profile needs to be understood alongside its limits and exposure over time.
CPM: what is the function permitted to do?
The Consequence Permission Matrix (CPM) records the permitted mode for a function across the relevant consequence classes. It uses four states:
- A, Authorised: the function may act within the class, subject to its declared OAL, purpose, limits and controls.
- H, Human-gated: the function may analyse, recommend or prepare an action, but an identified person must give informed, timely authorisation before the consequential change.
- M, Monitor only: the function may observe, detect and alert, but cannot alter, authorise, commit or materially steer the consequential process.
- X, Excluded: there is no authorised operational route for the function to affect that class. Controls should enforce that exclusion.
These are permissions, not grades of goodness. A human approval step is not automatically effective: it can become perfunctory, or the person approving may lack the information or time needed to make a meaningful decision. Monitoring also has effects of its own, including through observation and alerting. The profile describes intended boundaries; it does not certify that those boundaries are safe or acceptable.
Reading a profile in practice
A routine supplier-payments function is given as an example in the paper:
C1:A · C2:A · C3:H · C4:X
In plain English, the function may act autonomously within declared limits for limited and material consequences. Major consequences require informed human approval, and the function has no authorised route to critical consequences.
The OAL still matters. The paper’s example sets routine supplier payments at OAL-4, or Delegated. That does not mean the function may act without limits. Its mandate, transaction boundaries, aggregate exposure and controls still need to be specified.
For employment candidate-screening support, the paper gives a different profile: OAL-1, with C1:M, C2:M, C3:X and C4:X. Here the function is advisory; it may monitor within the first two consequence classes, but it has no authorised route to major or critical consequences. The example illustrates the notation, not a sector-wide prescription. The paper stresses that classification depends on context, purpose, affected people and the credibility of potential adverse outcomes.
The supplied portfolio map also includes a safety monitor as an illustrative function. Its position and profile are there to help managers discuss authority, consequence and change over time, not to set a universal rule for safety systems.
The most restrictive boundary governs
OAL and CPM answer different questions, and they must be read together. OAL describes how independently a function may operate. CPM describes whether and how it may interact with each consequence class.
If the declared OAL would allow a function to act, but the relevant CPM state requires human approval, the approval boundary governs. If the state is Monitor only, the function may observe and alert but cannot make a consequential commitment. If it is Excluded, the operational route should not exist.
That rule (the most restrictive boundary governs) is useful only if it is reflected in the system’s real permissions. A written matrix cannot enforce itself. SACM’s paper points to controls such as transaction limits, restricted credentials, separate approval channels, write restrictions and emergency stops, alongside testing for boundary cases and indirect routes.
It also calls for a defined function, a named accountable owner, stated limits, a review window and an explanation of reversibility. In other words, the profile should be specific enough to check, not simply a reassuring label in a policy document.
A framework for discussion, not a certificate
SACM is presented as a proposed framework for research and practical evaluation. It is not a certification of safety, legal compliance or ethical acceptability, and the paper does not claim empirical validation. Consequence judgements can vary; harms may be delayed or difficult to reverse; and a four-class scheme cannot represent every dimension of risk.
Its value lies in giving organisations a structured way to ask a more precise question than “How autonomous is the AI?” What does this particular function do, which people or processes could be affected, and what route, if any, should it have to each class of consequence?
The Steiner AI Authority & Consequence Matrix is free and open to use under the Creative Commons Attribution 4.0 licence (CC BY 4.0). The SACM v1.1 paper sets out the framework and its limitations.
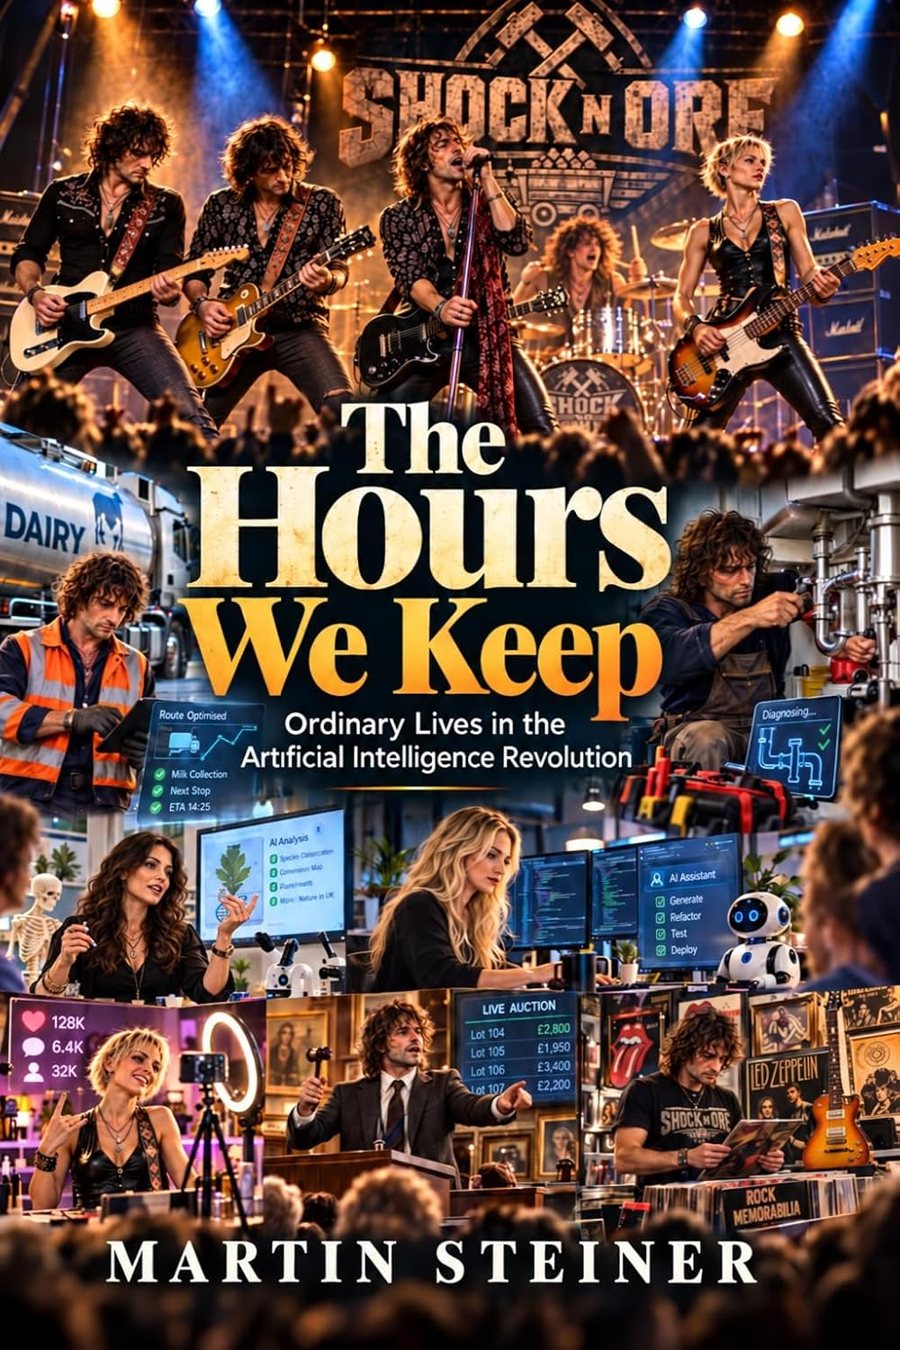
Martin Steiner also explores the human effects of AI through fiction in The Hours We Keep: Ordinary Lives in the Artificial Intelligence Revolution. Find out more on the author’s website, or see the book on Amazon: Kindle edition (ASIN B0HN4NJ89S) and paperback (ASIN B0HN62FXVC).
#TheHoursWeKeep #AIGovernance #ResponsibleAI #AIandSociety